
app) and the API (backend) — alongside a PostgreSQL database. This guide deploys all three with Docker Compose and connects your first supervisor.
Prerequisites
Docker + Compose
A host with Docker Engine and the Compose plugin.
Registry access
Credentials for the registry that hosts the Celum images.
OIDC application
A client registration with your identity provider (client ID, secret, issuer).
TLS + DNS
Two hostnames (app + API) terminating TLS at a reverse proxy.
Angle-bracket values below are placeholders —
<tenant-id>, <version>, <registry>, and so on. Substitute the values for your deployment; nothing here is a working default.1. Configure environment
Create a.env file next to your docker-compose.yml. Compose interpolates these values into the stack.
.env
Register
OIDC_REDIRECT_URL (https://<your-api-host>/auth/callback) as a redirect URI on your OIDC application.2. Define the stack
docker-compose.yml
FRONTEND_URL reaches the app service on port 3000 and BACKEND_PUBLIC_URL reaches the backend service on port 8080.
3. Start the stack
What happens on first load
1
Sign in
Unauthenticated requests are redirected to sign in through your OIDC provider. On return, the backend issues a signed session cookie.
2
Default supervisor
The root route opens the first supervisor you can access, at
/s/{supervisor}/. While no supervisor is registered you land on /welcome, which sends you to Settings → Kubeconfigs. If supervisors exist but IAM grants you none of them, you land on /no-access.3
Grant access
With
IAM_ENABLED=true, access is governed by IAM. A fresh database ships an Administrators group carrying the K8sGateAdmin policy, mapped to the OIDC claim value krn:celum:admin — assign that claim to yourself, or edit the group to match a claim you already have. See Authentication & IAM.4. Register your first supervisor
Celum reads no kubeconfig files. A supervisor is a kubeconfig registered in the dashboard and kept in the database. After you sign in, Celum opens on Welcome to Celum: drop the kubeconfig there, or upload it under Settings → Kubeconfigs. Register a supervisor walks through it.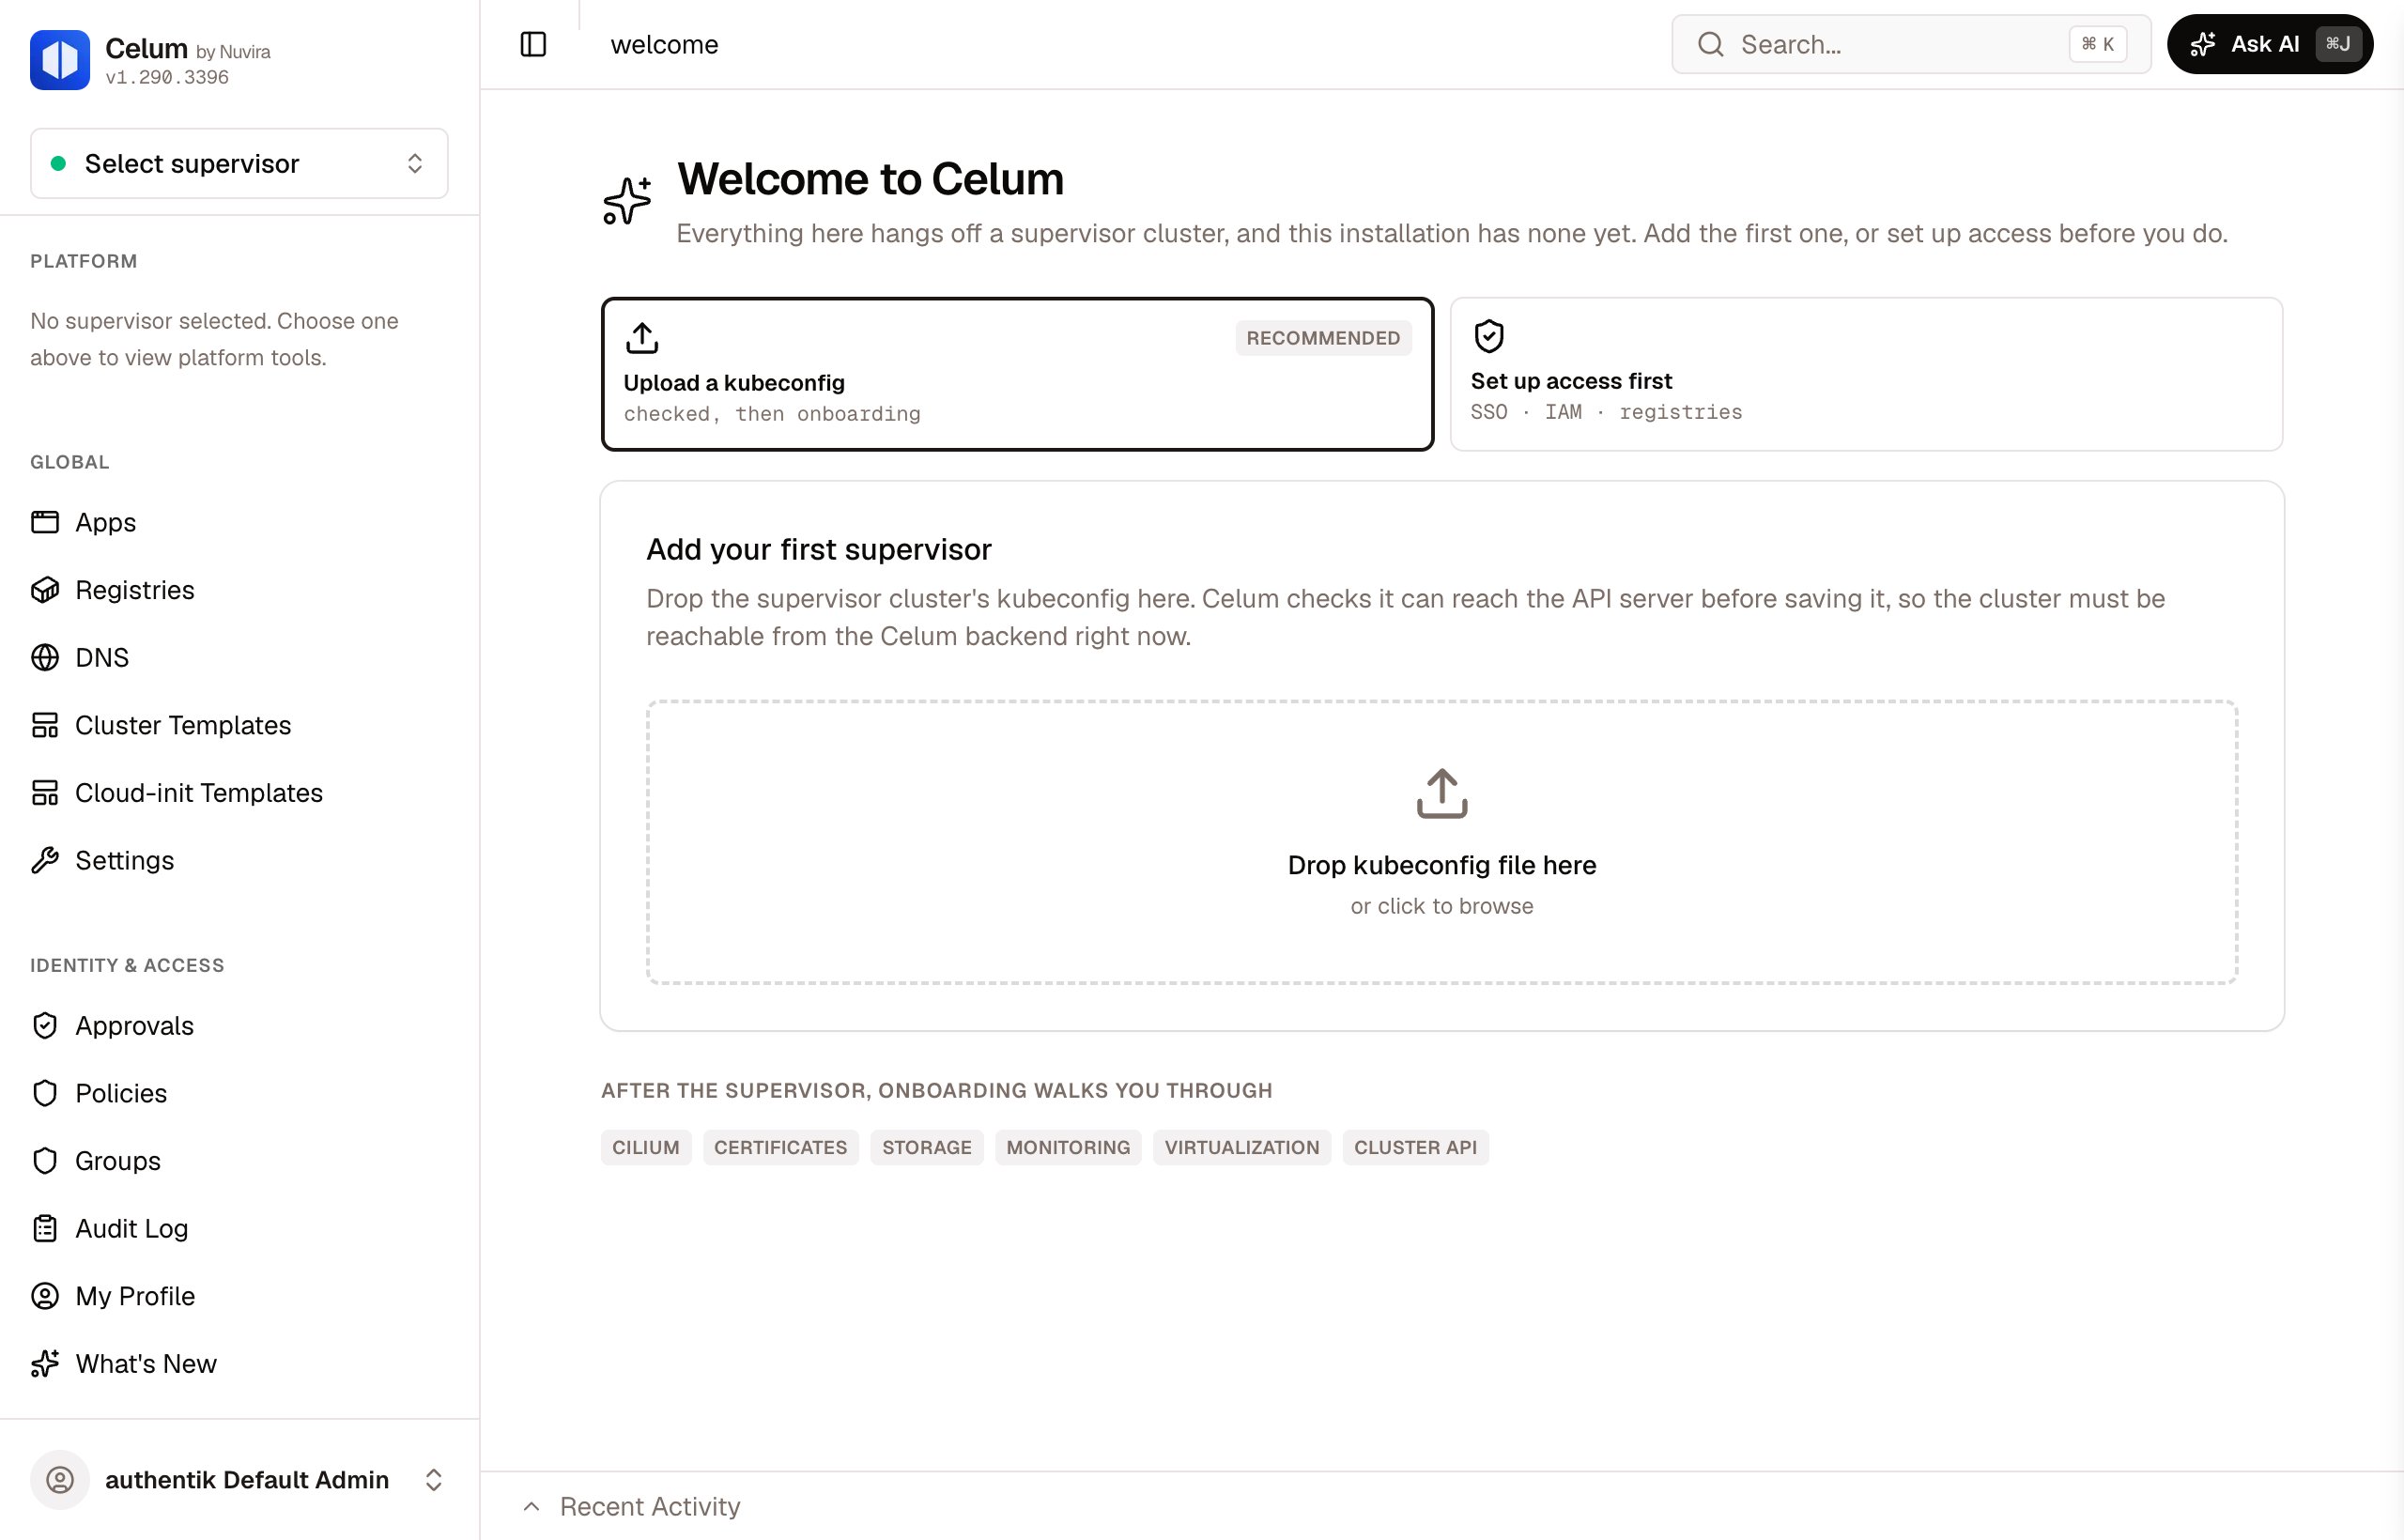
The first page while no supervisor is registered
What commonly goes wrong
Next steps
Authentication & IAM
Configure OIDC mapping and policies in depth.
Supervisors & clusters
How Celum discovers supervisors and what it reads from them.
Create a cluster
Provision a tenant cluster from a template.
Environment variables
Every variable the backend and dashboard read.