
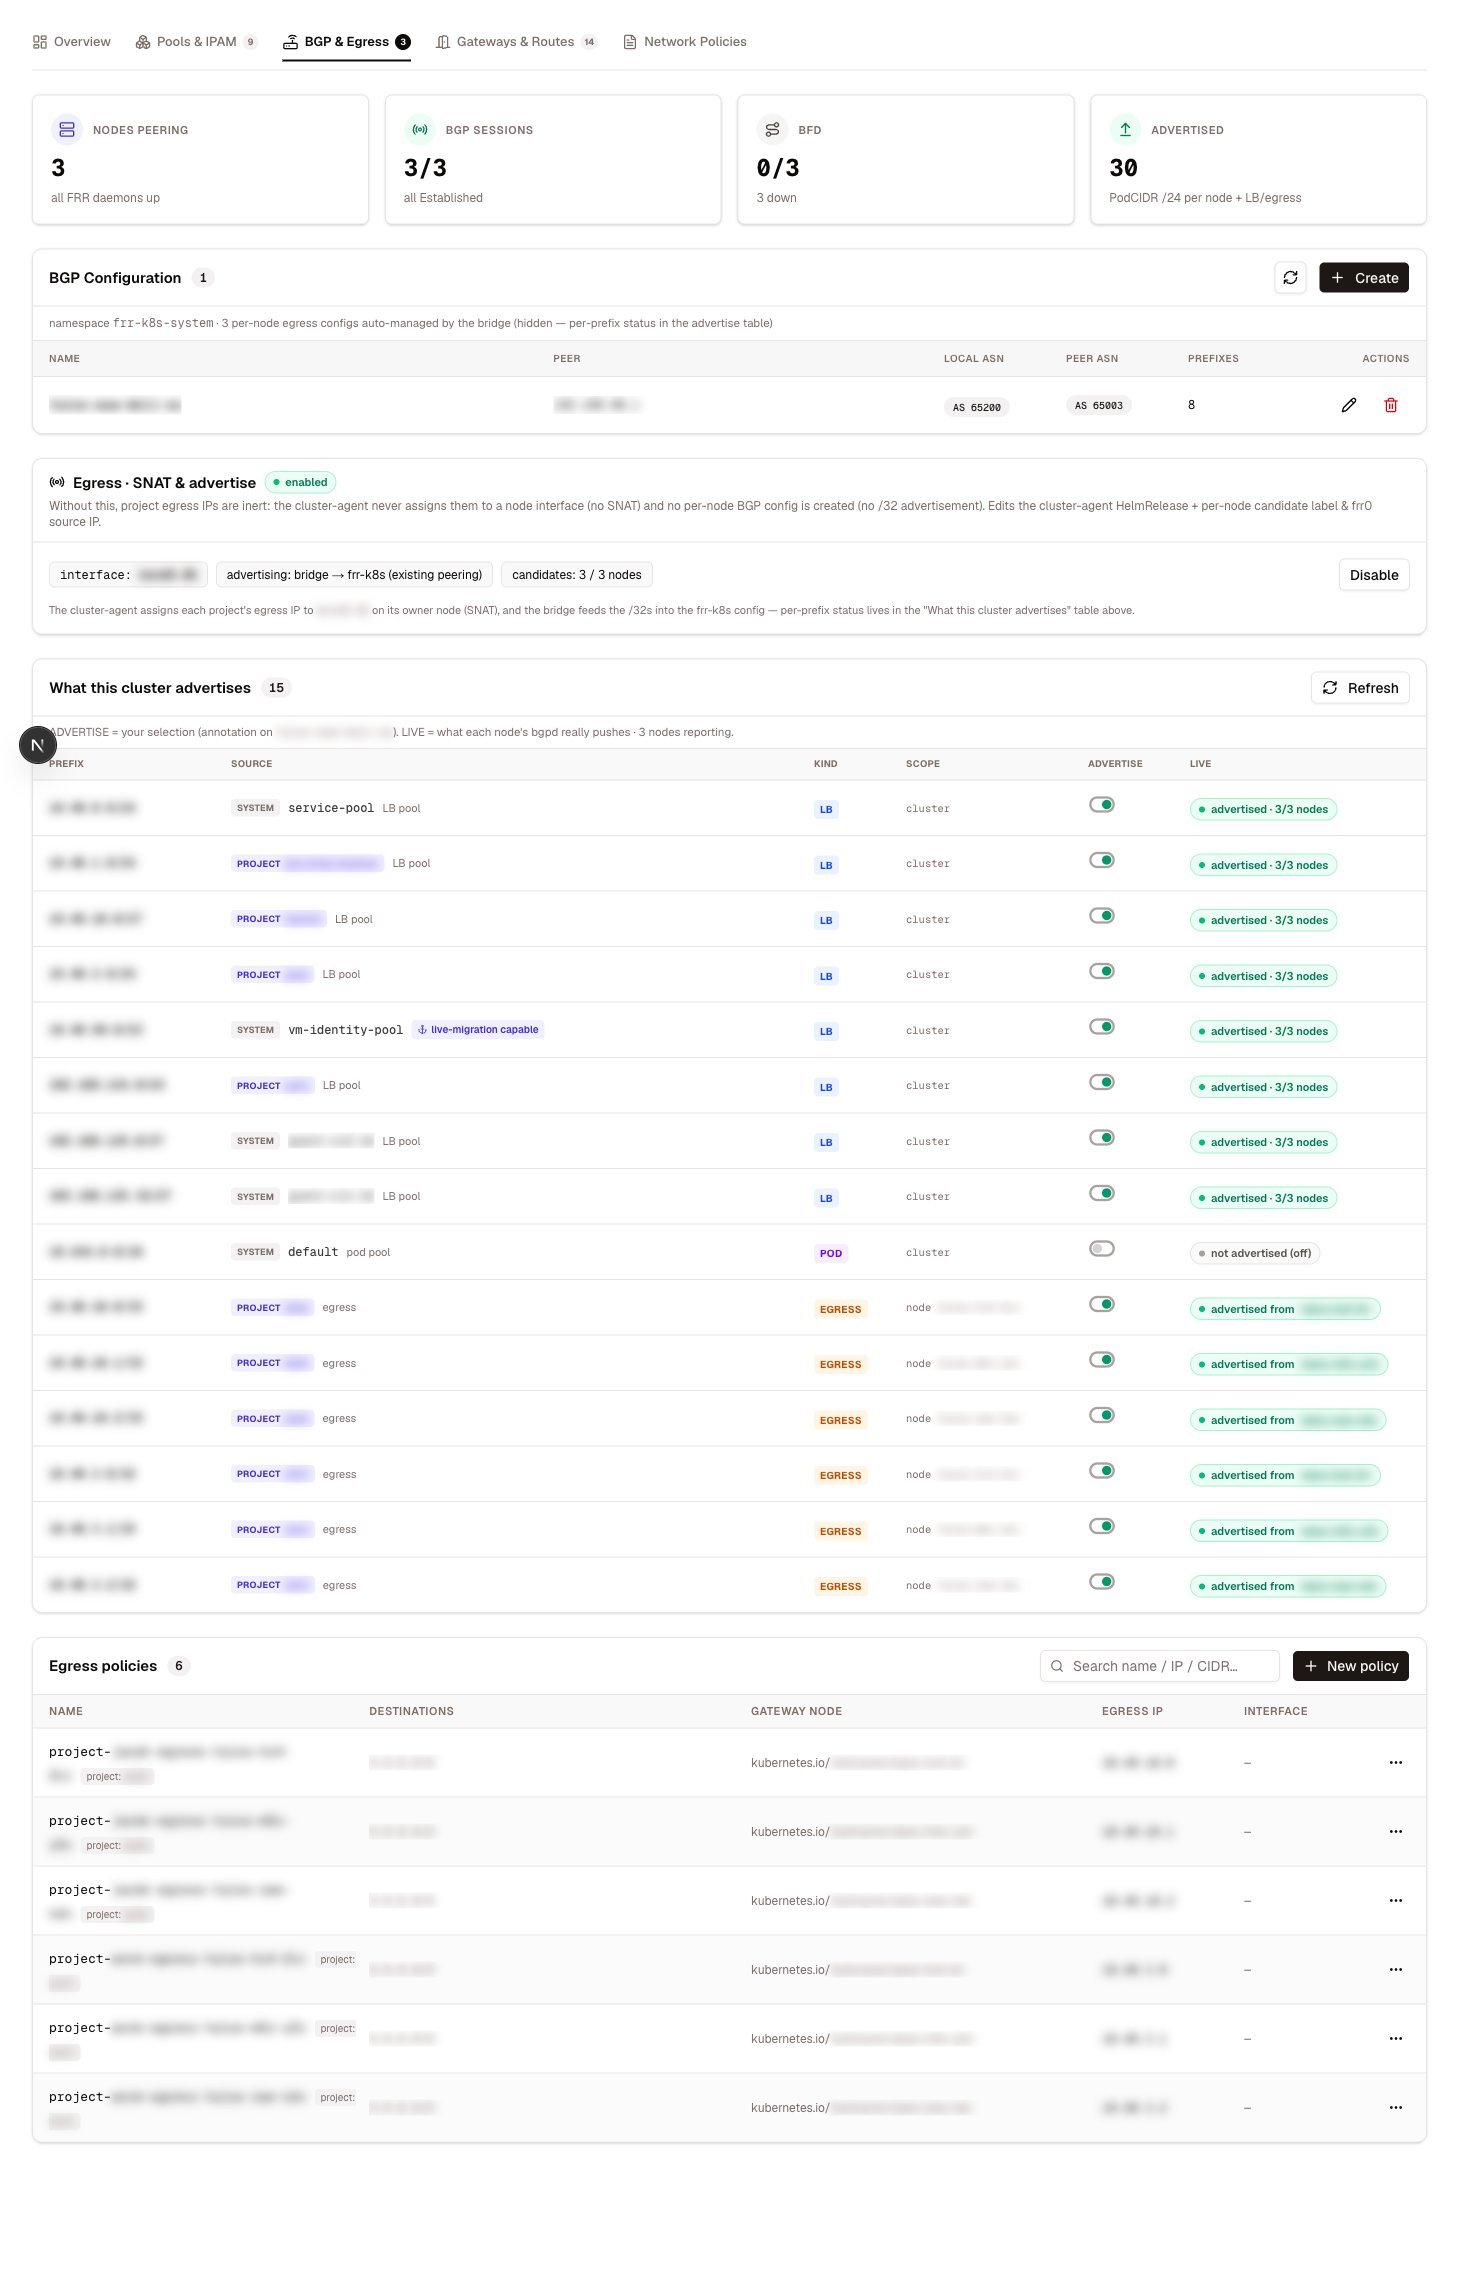
BGP engines
The view adapts to the BGP engine the supervisor runs — the engine pill in the page header tells you which:
Whichever engine is active, the same two surfaces render: per-node sessions and the advertise table.
Session monitoring
The session table shows one row per node and peer: peer address, local and peer ASN, session state and uptime, and the counts of advertised and received routes. A healthy row looks like this:
Anything other than
Established means that node is not exchanging routes. A node whose session is down stops carrying traffic for advertised prefixes — with more than one node peering, the fabric routes around it; with one, the prefix goes dark. Expanding a node also shows the routes it advertises and receives, with next hop and best-path markers.
The advertise table
The advertise machinery has several layers — candidate prefixes from live objects, the operator’s selection, the engine’s expansion, and what each node’s BGP daemon actually pushes. The advertise table flattens all of it into one row per prefix:
The Live column is the drift detector:
Two rows from a healthy-but-imperfect three-node supervisor:
The second row is what
partial looks like in practice: the prefix is selected and two nodes push it, but the third does not — usually that node’s BGP session is down, or the engine has not converged yet. The session table above tells you which.
Flipping a row’s toggle updates the operator selection; the engine converges and the Live column confirms it. Project-sourced rows follow the owning project’s own advertise toggles — change them on the project, and the rows here follow. The Overview tab shows a snapshot of this same table.
BGP peers
On a supervisor whose BGP engine is FRR-K8s, the BGP Configuration card lists the peers you configured. Each peer is oneFRRConfiguration in frr-k8s-system. The card hides the per-node configurations that the cluster agent writes for egress addresses (bridge-node-*). Their prefixes show in the advertise table. The Cilium BGP control plane has its own peer card, and the form below is for FRR-K8s only. On that card, Add peer adds a peer with no address and an empty ASN. An empty ASN means Cilium accepts any ASN the peer announces. Apply refuses a peer until it has an address or DefaultGateway auto-discovery.
- Dashboard
- API
- MCP
Networking → BGP & Egress → BGP Configuration → Create opens Create BGP peer. The pencil on a row opens the same form for that peer. The bin deletes the peer after you confirm.
The password never goes into the object. The form sends it alongside the spec. If the supervisor has a working secret store, Celum keeps the password there. Without a secret store, Celum writes the Secret
<name>-md5 in frr-k8s-system directly (type kubernetes.io/basic-auth, key password). The peer refers to <name>-md5 through passwordSecret. When you edit a peer, leave the password empty to keep the stored one. Type it when you create the peer, because the form does not require it.
What the form writes. The form writes one router with one neighbor that advertises in mode: all, and a BFD profile named <name>-bfd. It never writes prefixes. The cluster agent owns prefixes and toAdvertise.allowed.prefixes and fills them from the advertise table. The FRR-K8s API has no field for inbound soft reconfiguration, so the form adds it as a raw FRR line: neighbor <address> soft-reconfiguration inbound.
Advanced (JSON). This tab edits the FRRConfiguration spec directly, for example to add more neighbors, more routers or other raw FRR configuration. When you switch to it from Form, it shows exactly what Apply will send. Switching back to Form is refused when the spec holds more than the form can show. A peer like that always opens in Advanced (JSON). Only Form sends the MD5 password. Apply refuses a spec in which a router, or a neighbor without dynamicASN, has no ASN above 0.
When you delete a peer, Celum removes its FRRConfiguration. FRR-K8s then closes the peer’s sessions on every node at once and withdraws what was announced to that peer and learned from it. You cannot undo this. To restore the peer, enter it again.
Egress
Egress is the outbound mirror of gateways: instead of traffic coming in through a shared address, workloads leave the cluster through designated gateway nodes with a dedicated source IP (SNAT). Use it when an upstream firewall allow-lists by source address, or when compliance requires attributable egress. This tab is the single home for all three egress surfaces.Candidate nodes
Egress gateways are label-driven: a node label marks which nodes are eligible to carry egress IPs, and the candidate-nodes card manages that label declaratively — tick the nodes that should be candidates, and the platform labels exactly those. The same candidate set drives the per-node spread preview in project creation, the agent that places egress IPs on nodes, and the gateway selection in egress policies, so there is one source of truth.Egress HA
With a single candidate node, that node is a single point of failure for every egress IP it carries. The Egress HA section configures BGP-backed failover for the egress path:- Egress interface — the interface egress IPs are placed on, typically a VLAN subinterface of the nodes’ bond.
- Local ASN and AS-path prepend count — how the egress speakers present themselves to the upstream, and how strongly standby paths are depreferenced.
- Upstream peers — the routers the egress nodes peer with: address, remote ASN, optional eBGP multihop and BFD per peer. A new peer starts with neither, and Save asks for both.
- BFD timers — shared receive/transmit intervals and multiplier. At 50 ms / 50 ms with a multiplier of 3, a dead node is detected in roughly 150 ms — the egress IP moves before applications notice.
- Per-node settings — the candidate toggle and the BGP source address each node peers from.
Egress HA configures the platform’s own BGP speaker on the candidate nodes — it is independent of the cluster-wide BGP engine settings above, because failover needs per-node advertise and withdraw that a cluster-scoped configuration cannot express.
Egress policies
The policy table lists everyCiliumEgressGatewayPolicy. New policy creates a policy and Delete in a row’s menu removes it. You cannot edit a policy: to change one, delete it and create it again. A policy says: traffic from these pods to these destinations leaves via this gateway node with this source IP.
A sanitized policy, as the table shows it:
- Egress IP and Interface are mutually exclusive. With neither set, the default-route interface’s address is used.
- In-cluster destinations are automatically excluded, even when they fall inside the destination CIDRs.
- If the node selector matches several nodes, the first in lexical order wins — for deterministic placement, use the candidate machinery rather than broad selectors.
Create a policy
- Dashboard
- API
- MCP
BGP & Egress → Egress policies → New policy opens New egress policy:
- Name: required.
- Destination CIDRs: one per line, starting with
0.0.0.0/0. At least one is required. - Excluded CIDRs: optional, one per line.
- Namespace: leave it empty to match every namespace. Celum writes it as the
io.kubernetes.pod.namespacelabel in the pod selector. - Pod selector: optional
key=valuelines. A pod must match all of them. - Gateway node selector:
key=valuelines, at least one. It starts asnuvira.dev/egress-gateway-candidate=true, the label that the candidate-nodes card manages. - Egress IP: optional. Pick Node’s own IP, the default, which leaves the field empty, or one of the free addresses that the picker offers from the egress band of the supervisor’s address plan. Other… lets you type an address. The form keeps Create disabled while a typed address is not a single IPv4 address or overlaps an address or range that the plan records as held. An address outside the egress band also keeps Create disabled until you turn on Place it outside the plan. The address must be routed to the gateway node, normally as a
/32advertised over BGP. If the fabric does not route the address back, the replies are lost. - Interface: optional. The NIC that carries the egress IP.
Only the form checks the egress IP. Nothing on the server checks
egressIP against the address plan or for overlaps. An API call takes any address, and so does the form when it cannot read the address plan (reading it needs cilium:GetState). The picker is then a plain text field and says that nothing checks what you type for overlaps.Policies generated from a project’s egress configuration appear in the table but are read-only there — they carry the owning project in their labels and follow the project lifecycle. A project spreading several egress IPs across gateway nodes materializes as one such policy per node/IP pair. Edit the project, not the policy.
Permissions
Both are scoped to
krn:celum:supervisor:<supervisor>:cilium:*.
Related
Pools & IPAM
The pools whose prefixes populate the advertise table.
Project networking
The per-tenant intent behind read-only policies and project advertise rows.
Gateways & Routes
The inbound counterpart to egress.
Networking overview
The engine model and the Overview tab’s advertise snapshot.